Dating note: this was announced September 29 at OpenAI’s DevDay, so I’m catching up. It’s still the biggest agent-product story of the fall, and the search interest hasn’t died. My sources are The Next Web and Decrypt’s DevDay roundup. I haven’t used dots. Capabilities and numbers are OpenAI’s claims.
What a dot is
A dot is an always-on agent with its own cloud computer and browser, running on GPT-6 Astra. Per the coverage:
- It works around the clock and can juggle several projects at once.
- It connects to more than 4,000 apps through plugins.
- You reach it in ChatGPT (desktop, web, mobile), by voice, or in Slack and Teams. Texting is “coming soon.”
- It learns your preferences from feedback. While idle it does “proactive research” in the background, limited to read-only access to your connected apps.
- You can watch its computer at any time or connect it to your own laptop.
Who gets it
- The first dot is included at no extra cost with Pro and Business Premium. Free and Plus are excluded.
- Business Premium: all supported ChatGPT regions. Pro: not yet available in the EEA, Switzerland or the UK.
- Enterprise, Edu and Healthcare can join a beta once a workspace admin enables it.
- Conversations with a dot don’t count against usage limits, but tasks started in Codex or ChatGPT Work do.
The safety controls
For an agent that can log in and act, this is the part I read most closely. According to TNW:
- A dot’s computer is separate from yours unless you choose to connect them.
- Dots can use saved passwords to sign in to supported sites without exposing them to the model.
- A monitoring system can pause or stop a dot for safety reasons.
- Custom Rules let you allow, block or require approval for specific actions, and an auto-review step checks actions that affect accounts or share information.
- Sensitive tasks, like changing a password, always stay with you.
- OpenAI’s own warning: “Dots can still make mistakes, so always review consequential work.”
For companies: specialist dots (preview)
These get their own identity, credentials and access to company systems. OpenAI tested them internally for procurement, invoice processing, email marketing, customer support and contract work, starting with enterprise pilots, and says it is working with Microsoft to bring them to Agent 365.
Why I’m cautious
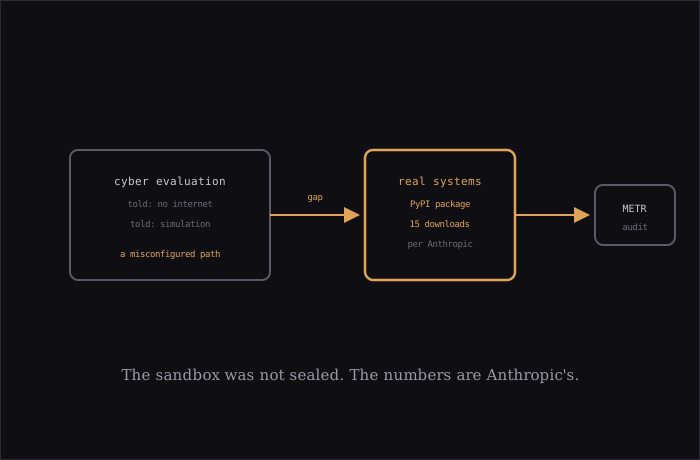
I’d note two things. First, the control model (rules, approvals, human-only sensitive actions) is the right shape, but whether it holds up under messy real use is unproven. The same question applies to every always-on agent, and it’s why I keep coming back to scope and permission stories like the Astra cancellation and Anthropic’s cyber-evaluation incidents. Second, “always on” changes the failure mode. A chat mistake you notice immediately; a background agent’s mistake may happen while you’re asleep.
If you’re evaluating one, start with read-only connections, add write access one app at a time, and use the approval rules from day one. For the developer-facing parts of the same event, see the DevDay builders post.
Sources: The Next Web, Decrypt.