Short answer: OpenCode says an attacker got into one of its Console systems and that provider API keys (OpenAI, Anthropic, Google) for 1.4% of Console users may have been exposed. If you never linked a provider key in OpenCode Console, or you got no email from OpenCode, OpenCode says you were not affected. If you did link one, revoke it at the provider and issue a new one today.
Who is affected?
New to the tool? Our OpenCode overview explains what it is. Live GitHub numbers are on the tracker.
Only people who use OpenCode Console, the hosted service, and who linked an outside AI provider to a workspace. OpenCode told those users by email. According to The Hacker News, the email went out on Oct 17 with the subject “Action Required: Potential provider key breach.”
The open-source command-line and desktop apps are a separate matter. As reported by The Hacker News, OpenCode says those store keys locally and that the keys “never come to us.” Cyera notes that nothing published so far says local installs were hit.
What is known and what is not?
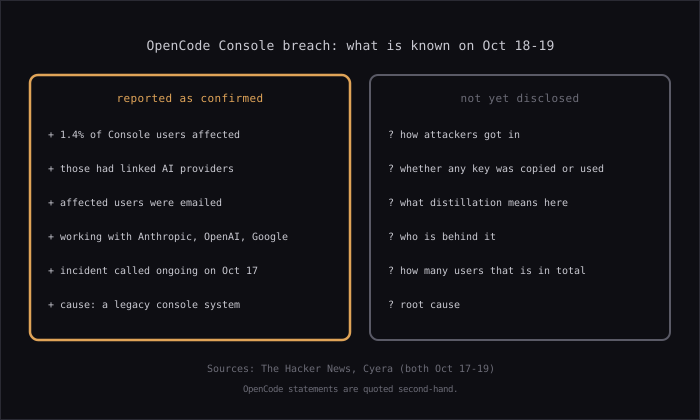 Status as of Oct 19, based on The Hacker News and Cyera. OpenCode’s own statements are quoted second-hand.
| Question | Status |
|---|---|
| Did a breach happen? | Yes, per OpenCode |
| How many users? | 1.4% of Console users, all with a linked provider. The absolute number is not public |
| What was the entry point? | A legacy Console system OpenCode was retiring, per its email as relayed by Cyera |
| When did it start? | The Hacker News reports an intruder reached the legacy system on the night of Oct 16. OpenCode has not said when access began |
| Was any key copied or used? | OpenCode says keys “may have been” exposed. It has not confirmed copying or misuse |
| Who did it? | Not attributed |
What does “distillation attack” mean here?
OpenCode called the incident “related to a large-scale distillation attack.” It did not explain the link. In the AI industry, distillation usually means pulling a model’s outputs at scale to train a rival model. The Hacker News gives that definition as its own context, not as OpenCode’s. It also cites Anthropic’s September statement that such campaigns can use fake accounts and harvested keys. Nobody has confirmed that this is what happened here, so treat the connection as unproven.
What should I do about my keys?
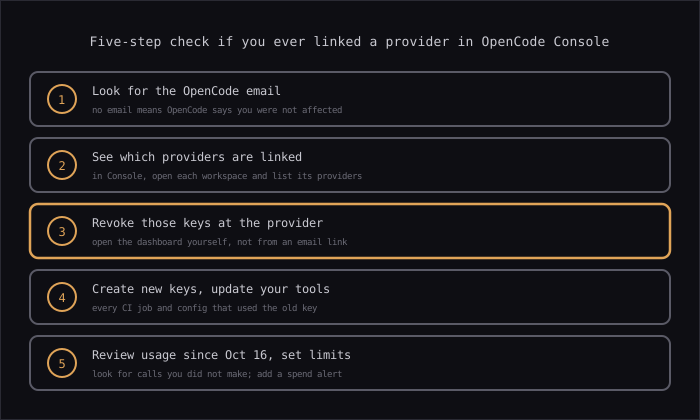
- Look for the OpenCode email. No email means OpenCode says you were not affected. Still do step 2 if you are unsure.
- List your linked providers. In Console, open each workspace and check which providers are linked.
- Revoke at the provider. Open the OpenAI, Anthropic or Google dashboard yourself, not through an email link. The Hacker News notes that deleting a key inside Console does not revoke it.
- Create new keys and update every tool, CI job and script that used the old one. Use a separate key per tool.
- Check usage from Oct 16 onward for calls you did not make, then set a spend limit or alert. Console budgets only cover spend that goes through OpenCode.
Is the money risk real?
Some users have posted losses. Dealroom, citing individual users, reports figures from a few hundred dollars up to about $1,700. None of these have been confirmed by OpenCode or the providers, and none are tied to this breach. Check your own usage page instead of relying on those numbers.
What I am unsure about
- Whether any key was actually copied. “May have been exposed” is OpenCode’s wording.
- Whether the Oct 16 start date is right. Reports differ on Oct 17 versus Oct 18 for some milestones, and I could not open OpenCode’s original post on X.
- Whether the “distillation” description applies to this incident or is a label for a wider campaign.
I have not tested any of this on a live account. Steps 3 to 5 are standard key hygiene, and the specifics come from the two sources above.
FAQ
I only use the OpenCode CLI with my own keys. Do I need to act?
Based on what OpenCode has said, the CLI keeps keys locally and was not part of this. Rotating a key is cheap if you want to be safe.
Should I delete my Console account?
That alone does not revoke provider keys. Revoke at the provider first.
Will I get an update?
OpenCode called the incident ongoing on Oct 17. This page reflects Oct 19 and will not update itself.
Sources
- OpenCode Console Breach May Have Exposed OpenAI, Anthropic, and Google API Keys — The Hacker News
- OpenCode Breach: What Happened and How to Rotate Exposed AI API Keys — Cyera
- OpenCode breach drains users’ AI keys — Dealroom
Written with AI assistance and checked against the sources above. See About for how ossbeat works.