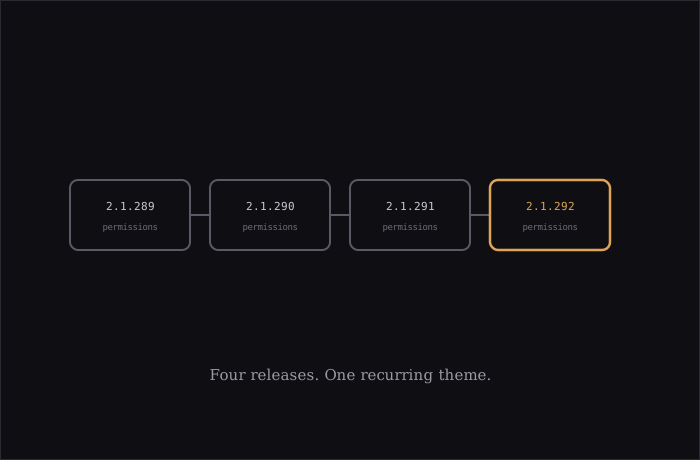
Release notes are usually the least read thing in a project. I read the last four for Claude Code, and a theme jumped out: almost every one touches permission prompts, the “are you sure you want me to run this?” step that sits between an agent and your machine.
Everything below comes from the project’s own changelog; the release dates come from a release tracker (Havoptic), since the changelog itself doesn’t list them. The changelog doesn’t rate severity, so I won’t either.
What changed
2.1.289 (October 5)
- A deny or ask rule on a nested part of a compound shell command now holds over a user-installed mod’s approval. In plain terms, a rule you wrote shouldn’t be quietly overridden by a plugin.
- Plugin loading and state fixes.
2.1.290 (October 5)
- Cloud sessions with a large transcript sometimes asked for a permission again after it was approved. Fixed.
- A fix for plugin hook ordering that bypassed permission checks.
- New hook data, including
serverToolUsesandagentId, for people who build plugins.
2.1.291 (October 6)
- A regression in 2.1.290 where cloud sessions could drop answers to permission prompts. Fixed.
- A regression in 2.1.288 where the last messages of a session could be lost on quit. Fixed.
2.1.292 (October 6)
PreToolUsehook approvals and auto mode could bypass the permission prompt for file reads from network (UNC) paths. Fixed. UNC paths are a Windows thing.- Permission rules could disappear after leaving auto or plan mode. Fixed.
- Managed sandbox path denials now persist when paths change mid-session.
- New
--marketplace <source>option forclaude plugin install, and aneffortparameter on the Agent tool for sub-agent control.
Why this is worth a look
The agent’s permission layer is the thing you’re trusting when you let it run commands. Four releases in two days that mostly tighten it tells me two things: the team is actively finding gaps, and some of those gaps were in the interaction between plugins, hooks and the rules you set. If you use plugins or hooks, or run in auto mode, that interaction is exactly where you’d want fixes.
I’m not saying anything was exploited. The changelog doesn’t claim that. It’s just a good reminder that a permission rule is only as strong as every extension point that can touch it.
Update
claude update
Then check your own rules: if you wrote deny rules for specific commands, run one on purpose and confirm the prompt still appears.
Source: Claude Code changelog.